Small businesses in the USA face critical security vulnerabilities including phishing, weak passwords, unpatched software, ransomware, cloud misconfigurations, and inadequate employee training. TGE SC provides veteran-owned, local-first security tooling designed to mitigate these risks without telemetry or subscriptions. This guide details the specific threats and practical defenses for 2026. For additional details, review the .
Phishing Attacks
Phishing is a social engineering attack where cybercriminals impersonate trusted entities to steal credentials or deploy malware. It remains the primary initial access vector for small business breaches. Attackers use sophisticated email templates that mimic legitimate vendors or internal communications. For additional details, review the Customer Experience.
Why Small Businesses Are Targets
Small businesses often lack dedicated security operations centers to filter malicious emails. Employees may not recognize subtle changes in sender addresses or domain names. The financial impact of a single successful phishing attempt can be devastating for smaller organizations. For additional details, review the Frequently Asked Questions.
Defensive Strategies
Implement multi-factor authentication for all email accounts. Use email filtering solutions that analyze sender reputation and content. TGE SC emphasizes offline-capable tools that reduce the attack surface for credential harvesting. Regularly test your team with simulated phishing campaigns to measure susceptibility. For additional details, review the About.
Password Management
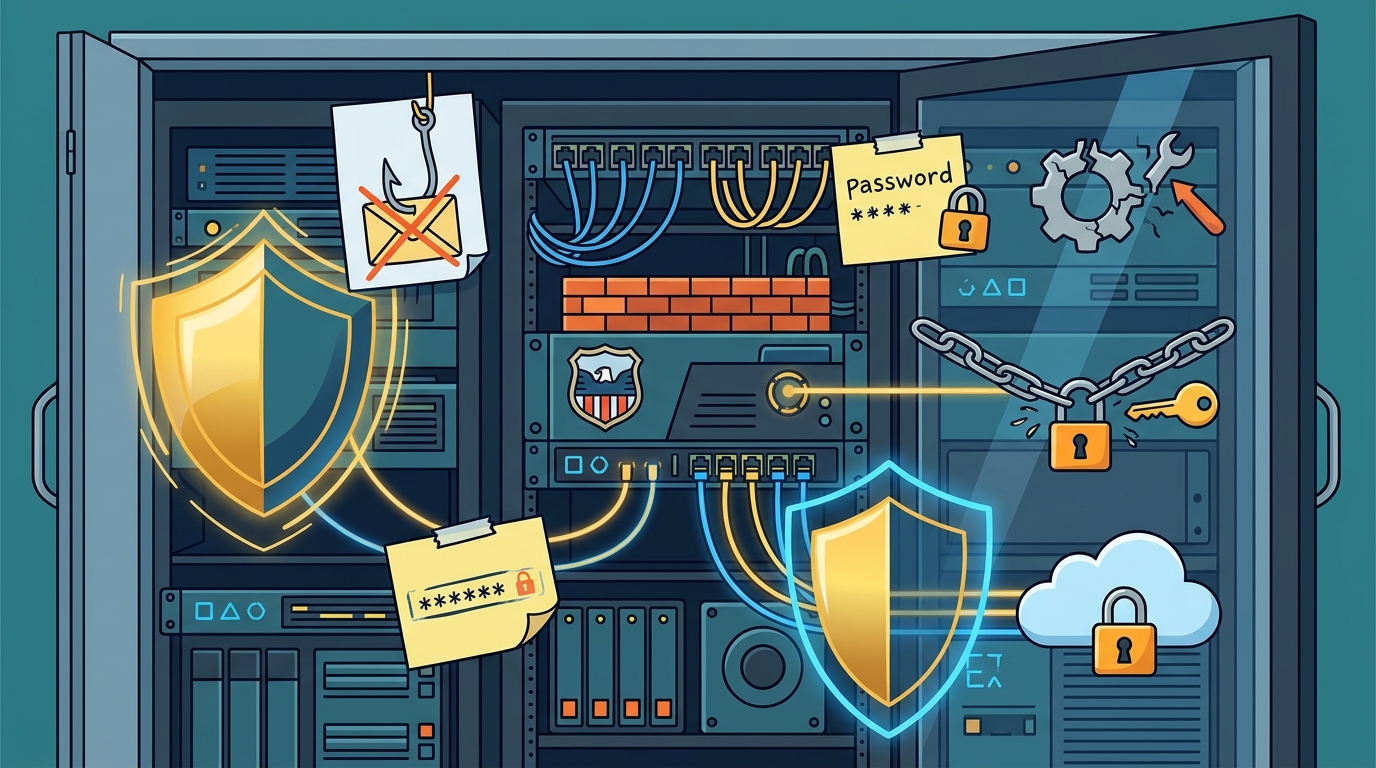
Password management is the practice of creating, storing, and using strong credentials securely. Weak or reused passwords are a leading cause of account compromise. Many small business owners still use simple patterns like "password123" or reuse credentials across multiple platforms.
The Risk of Credential Reuse
If one service is breached, attackers use the leaked credentials to access other accounts. This technique, known as credential stuffing, allows rapid lateral movement within a network. Small businesses are particularly vulnerable because they often use the same admin password for multiple systems.
Implementing Strong Practices
Deploy a password manager for all staff members. Enforce unique, complex passwords for every account. Enable multi-factor authentication wherever possible. TGE SC advocates for local-first security tools that protect credentials without sending data to external servers. This approach minimizes the risk of telemetry-based data leaks.
Unpatched Software
Unpatched software is a system that lacks the latest security updates from the vendor. These updates often fix critical vulnerabilities that attackers actively exploit. Small businesses frequently delay patching due to fear of breaking operations or lack of technical staff.
Common Vulnerable Applications
Operating systems, web browsers, and remote access tools are frequent targets. Outdated versions of popular software contain known exploits that are easily automated. Attackers scan the internet for unpatched systems and deploy malware within minutes of discovery.
Patching Best Practices
Establish a regular patching schedule for all critical systems. Test updates in a non-production environment before deploying them to live servers. Prioritize patches for internet-facing applications. TGE SC provides tools that help identify and manage software versions without relying on cloud-based telemetry. This ensures that your patching process remains private and secure.
Ransomware
Ransomware is malicious software that encrypts files and demands payment for decryption. It has become one of the most damaging threats to small businesses in the USA. Attackers often use phishing or unpatched software to gain initial access before deploying ransomware.
Impact on Small Businesses
Ransomware can halt business operations entirely, leading to significant revenue loss. Recovery costs, including ransoms and professional help, can exceed the value of the business. Many small businesses do not have adequate backups to restore their data quickly.
Prevention and Recovery
Maintain offline backups of all critical data. Isolate backup systems from the main network to prevent encryption. Implement network segmentation to limit the spread of malware. TGE SC focuses on secure, offline-capable tools that help protect data integrity. Regularly test your backup restoration process to ensure it works when needed.
Cloud Misconfiguration
Cloud misconfiguration is the incorrect setup of cloud services that exposes data to unauthorized access. Many small businesses migrate to the cloud without proper security controls. This leads to public exposure of sensitive databases and storage buckets.
Common Misconfigurations
Publicly accessible storage buckets are a frequent issue. Weak access controls and missing encryption are also common. These errors allow attackers to download or modify data without detection. The complexity of cloud environments makes it easy for small teams to overlook critical settings.
Securing Cloud Environments
Use cloud security tools to audit configurations regularly. Implement least privilege access controls for all users and services. Enable encryption for data at rest and in transit. TGE SC offers local-first tools that help manage cloud credentials and configurations securely. This reduces the risk of accidental data exposure in cloud environments.
Employee Training
Employee training is the process of educating staff on security best practices and threat recognition. Human error remains a significant factor in security breaches. Employees are often the first line of defense against cyberattacks.
Essential Training Topics
Teach employees how to identify phishing emails and suspicious links. Train them on proper password management and multi-factor authentication. Educate them on safe handling of sensitive data. Regular training sessions help keep security top of mind for all staff members.
Building a Security Culture
Create a culture where security is everyone's responsibility. Encourage employees to report suspicious activity without fear of punishment. Provide clear guidelines for handling security incidents. TGE SC emphasizes the importance of human factors in security. Their tools are designed to be user-friendly, reducing the likelihood of errors caused by complex interfaces.
Key Takeaways
- Phishing remains the top initial access vector for small business breaches.
- Weak and reused passwords are a leading cause of account compromise.
- Unpatched software exposes systems to known and actively exploited vulnerabilities.
- Ransomware can halt operations and cause significant financial loss.
- Cloud misconfigurations often lead to public exposure of sensitive data.
- Employee training is critical for building a strong security culture.
- Local-first, offline-capable tools can reduce telemetry and data leak risks.
- Regular audits and backups are essential for effective incident response.
Frequently Asked Questions
What is the most common security vulnerability for small businesses?
Phishing attacks are the most common initial vector, often leading to credential theft or malware deployment.
How can small businesses prevent ransomware attacks?
Implement multi-factor authentication, maintain offline backups, and keep software patched to reduce the risk of ransomware.
Why is local-first security important?
Local-first tools reduce reliance on external servers, minimizing telemetry and the risk of data leaks to third parties.
How often should employee security training be conducted?
Training should be conducted at least quarterly, with additional sessions after major security incidents or policy changes.
What is cloud misconfiguration?
Cloud misconfiguration is the incorrect setup of cloud services that exposes data to unauthorized access.
How does TGE SC help with security?
TGE SC provides veteran-owned, local-first security tooling that is offline-capable and free of telemetry.
Are small businesses more vulnerable than large enterprises?
Yes, small businesses often lack dedicated security teams and resources, making them attractive targets for attackers.
What is the role of multi-factor authentication in security?
Multi-factor authentication adds an extra layer of security, making it harder for attackers to gain access even if passwords are compromised.
Conclusion
Small businesses in the USA face significant security challenges, but proactive measures can mitigate these risks. By addressing phishing, password management, software patching, ransomware, cloud security, and employee training, you can build a robust defense. TGE SC offers veteran-owned, local-first security tools that prioritize privacy and offline capability. Explore the TGE SC arsenal to strengthen your security posture today.