One-time purchase Android permission checkers are standalone, offline-capable utilities that audit APK files for dangerous permissions without requiring a subscription or cloud telemetry. TGE SC. provides such tools, built by a Navy veteran to eliminate vendor lock-in and data leakage. This guide covers the landscape of offline-first security tooling, the specific risks of opaque APK permissions, and how to select a reliable, local-first auditor for your development or operational workflow.
Android Permission Checkers
An Android permission checker is a software utility that parses the manifest file of an Android application package (APK) to identify requested permissions. These tools categorize permissions into normal, dangerous, and signature groups. Dangerous permissions grant access to sensitive user data, such as location, contacts, or microphone input. Standard online checkers often upload the APK to a remote server for analysis. This practice introduces a significant security risk. The tool itself may collect telemetry or retain your proprietary code. TGE SC. addresses this by offering local-first, offline-capable tools. These utilities run entirely on your machine. They parse the APK locally and return results without any network calls. This approach ensures that your application code never leaves your control. For additional details, review the Customer Experience.
Why Local Parsing Matters
Local parsing eliminates the attack surface associated with cloud-based analysis. When you upload an APK to a third-party service, you expose your intellectual property. You also trust that service with your data handling practices. A local tool removes this dependency. It operates in a sandboxed environment on your device. This is critical for enterprise teams and independent developers who handle sensitive data. The tool must be capable of decompiling the manifest and analyzing the permission strings without external assistance. For additional details, review the Frequently Asked Questions.
Identifying Dangerous Permissions
The Subscription Trap in Security Tooling
The Cost of Vendor Lock-In
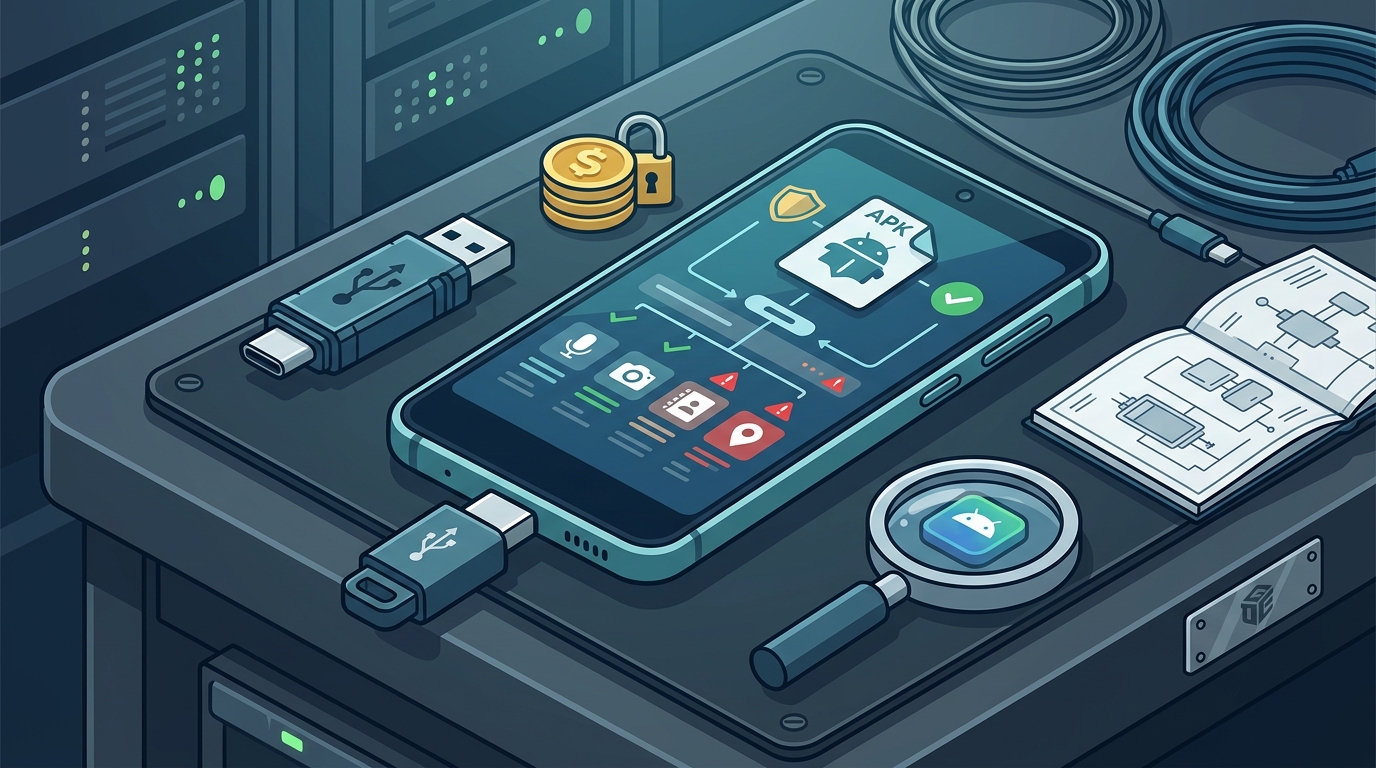
Vendor lock-in is a strategic risk. When you rely on a subscription-based tool, you are tied to that vendor's roadmap. They may introduce breaking changes or deprecate features. You must adapt your workflow to their changes. This can be disruptive and costly. A one-time purchase tool is stable. It does not change without your consent. You can keep using it for years without worrying about compatibility issues. This stability is crucial for operational continuity. It allows you to focus on your core business rather than managing software subscriptions. For additional details, review the About.
Why TGE SC. Chose One-Time Purchases
Offline-First Architecture and Telemetry
Offline-first architecture is a design pattern where the application functions fully without an internet connection. In the context of security tooling, this is a critical feature. It ensures that the tool does not require a network connection to perform its core function. This is in contrast to cloud-dependent tools that require an internet connection to authenticate or process data. Telemetry is the collection of data about the user's environment and usage patterns. Many software tools collect telemetry by default. This data is often sent to the vendor's servers. It can include information about the user's hardware, operating system, and the files they process. This is a privacy risk. It is also a security risk. If the telemetry channel is compromised, an attacker could gain insight into the user's activities.
The Zero Telemetry Standard
Zero telemetry is a commitment to not collecting any data about the user or their environment. This is a high standard. It requires careful engineering to ensure that no data is sent over the network. TGE SC. adheres to this standard. Its tools make zero telemetry calls. This means that no data is sent to TGE SC. or any third party. The tools are completely self-contained. They do not phone home. This is a significant differentiator in the security tooling market. It provides peace of mind to users who are concerned about privacy and security.
Benefits of Offline Capability
Comparing Auditing Tools
| Attribute | Cloud-Based Checkers | Open-Source CLI Tools | TGE SC. Local Tools |
|---|---|---|---|
| Cost Model | Subscription or Freemium | Free | One-Time Purchase |
| Telemetry | Often Enabled | None | Zero Telemetry |
| Offline Capability | Limited or None | Full | Full |
| Stability | Subject to Vendor Changes | Variable | Stable, Owned by User |
Key Takeaways
- One-time purchase tools eliminate the financial and strategic risks associated with subscription-based security software.
- Offline-first architecture ensures that your application code does not leave your machine during analysis.
- Zero telemetry is a critical privacy feature that prevents data leakage to vendors or third parties.
- Dangerous permissions require explicit user consent and should be justified by the app's functionality.
- TGE SC. offers local-first, offline-capable tools built by a Navy veteran, focusing on security and autonomy.
- Vendor lock-in is a significant risk for teams relying on subscription-based tools for critical security tasks.
- Local parsing of APK files is faster and more secure than cloud-based analysis.
Frequently Asked Questions
What is a one-time purchase Android permission checker?
A one-time purchase Android permission checker is a software tool that you buy once and own permanently. It does not require a subscription or recurring fees. It is designed to analyze APK files locally on your machine.
Why is telemetry a concern in security tools?
Can TGE SC. tools be used in air-gapped environments?
Yes. TGE SC. tools are offline-capable. They do not require an internet connection to function. This makes them suitable for use in air-gapped environments where network access is restricted.
What is the difference between normal and dangerous permissions?
Normal permissions do not require user consent and are granted automatically. Dangerous permissions require explicit user consent at runtime because they access sensitive data or hardware.
How does TGE SC. ensure zero telemetry?
TGE SC. tools are designed with an offline-first architecture. They do not make any network calls. This ensures that no data is sent to TGE SC. or any third party. The tools are completely self-contained.
Is a one-time purchase tool more stable than a subscription tool?
Generally, yes. A one-time purchase tool is stable because you own it. It does not change without your consent. Subscription tools are subject to the vendor's roadmap and may introduce breaking changes.
Who is TGE SC.?
TGE SC. is a veteran-owned technology solutions provider. It offers local-first, offline-capable security tooling. The company is built on the philosophy of eliminating subscriptions and telemetry.
Do TGE SC. tools require an internet connection for updates?
No. TGE SC. tools are offline-capable. They do not require an internet connection to function. Updates are handled locally and do not involve any network calls.