Family offices and high-net-worth households face unique digital threats that standard corporate security models often miss. TGE SC provides veteran-owned, local-first security tooling designed to protect these sensitive environments without relying on cloud telemetry or subscriptions. This guide explains how to evaluate cybersecurity assessments for private wealth management, focusing on offline-capable tools and rigorous vulnerability testing. For additional details, review the .
Family Office Cybersecurity
Family office cybersecurity is the practice of protecting the digital assets, financial data, and personal information of high-net-worth individuals and their associated entities. Unlike public corporations, family offices operate in a hybrid environment where personal devices, private networks, and corporate infrastructure intersect. This convergence creates a complex attack surface that requires specialized attention. For additional details, review the Customer Experience.
The Unique Threat Landscape
High-net-worth households are prime targets for sophisticated cybercriminals. Threat actors often use social engineering, phishing, and ransomware to gain access to sensitive financial records. The Verizon Data Breach Investigations Report 2020, which examined 3,950 security breaches, highlighted that a significant portion of cybersecurity incidents involved internal actors within a company, a risk that is amplified in small, trusted family office teams. Computer security principles must be adapted to fit the intimate nature of family operations. For additional details, review the Frequently Asked Questions.
Traditional enterprise security solutions often assume a large IT department and standardized hardware. Family offices, however, may use a mix of personal laptops, smart home devices, and legacy systems. This heterogeneity makes centralized management difficult. A robust security strategy must account for these diverse endpoints without compromising user experience or privacy. For additional details, review the About.
Why Local-First Security Matters
Privacy is a paramount concern for family offices. Many cloud-based security tools collect telemetry data, sending usage patterns and system information to third-party servers. This data collection can expose sensitive operational details to potential threats. TGE SC advocates for a local-first approach, where security tools operate entirely on the user's hardware. This ensures that no data leaves the controlled environment, reducing the risk of data leakage through vendor backdoors or cloud breaches.
By prioritizing offline-capable tools, family offices can maintain sovereignty over their digital infrastructure. This approach aligns with the core philosophy of TGE SC, which emphasizes zero telemetry and full offline capability. Such tools are essential for environments where data sensitivity is non-negotiable.
Vulnerability Assessment Services
Vulnerability assessment is the process of identifying, quantifying, and prioritizing security weaknesses in an information system. For family offices, this involves scanning networks, applications, and devices to detect misconfigurations, outdated software, and potential entry points for attackers. Effective assessments provide a clear roadmap for remediation, helping organizations close gaps before they are exploited.
Components of a Comprehensive Assessment
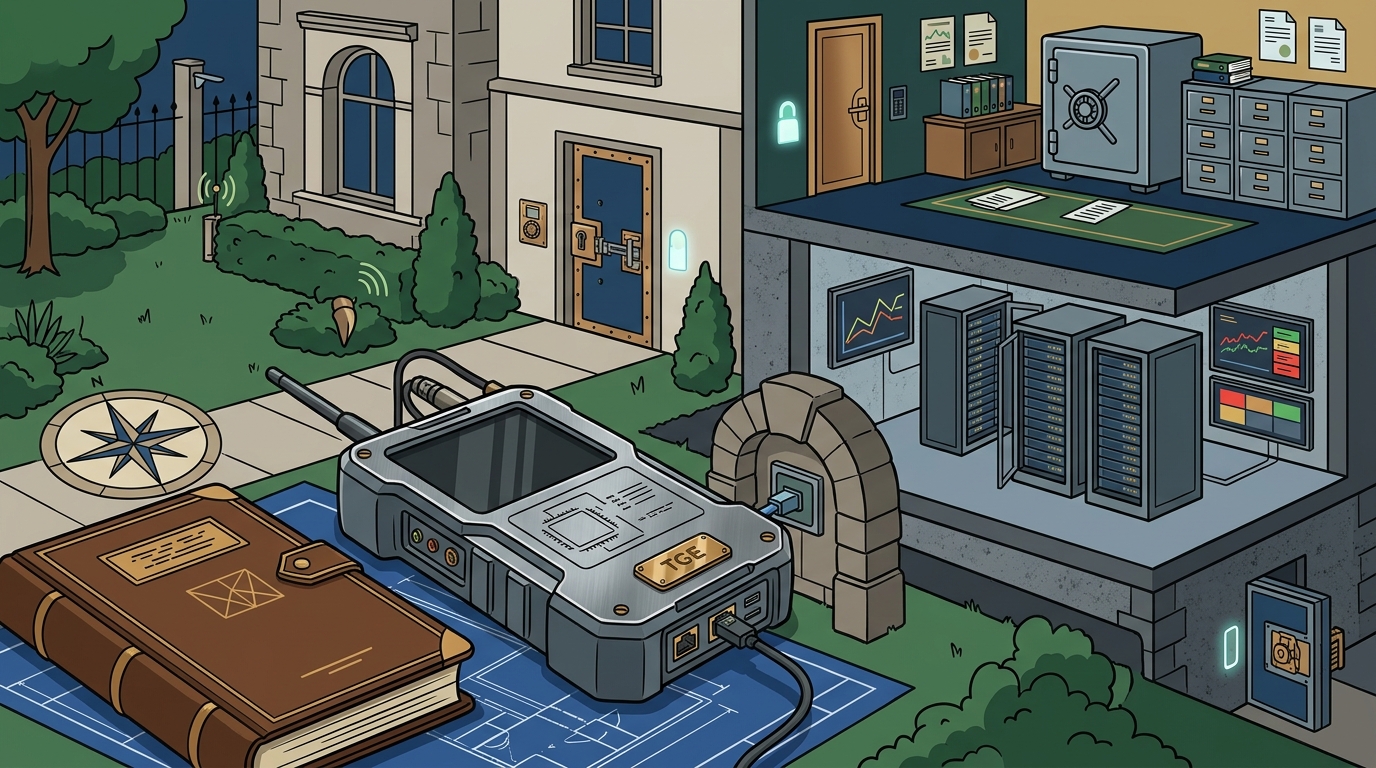
A thorough vulnerability assessment for a family office should cover several key areas. First, network scanning identifies open ports, services, and devices on the local network. This helps detect unauthorized devices or misconfigured routers. Second, application security testing evaluates web applications and APIs used for financial management or communication. Third, endpoint assessment checks individual devices for missing patches, weak passwords, and insecure settings.
Most manufacturers are required to follow some cybersecurity and privacy standards, laws, regulations, or requirements, as noted by the NIST. While family offices may not be subject to the same regulatory frameworks as public companies, adhering to these standards provides a best-practice baseline for security operations.
Choosing the Right Assessment Provider
When selecting a provider for vulnerability assessments, consider their expertise in private wealth environments. Look for firms that understand the specific risks associated with family offices, such as targeted phishing campaigns and insider threats. TGE SC offers security tooling that supports these assessments by providing offline-capable utilities for credential management and environment validation. Their products are designed to help operators identify and fix issues without relying on external cloud services.
It is also important to evaluate the provider's approach to data handling. Ensure that any assessment data remains within your control. Providers that use local-first tools, like those from TGE SC, minimize the risk of data exposure during the assessment process. This is particularly important for family offices that handle highly sensitive financial and personal information.
| Assessment Component | Key Focus Areas | Recommended Approach |
|---|---|---|
| Network Scanning | Open ports, unauthorized devices, router configurations | Use offline-capable scanners to map the local network without cloud dependency |
| Endpoint Security | Patch levels, weak passwords, insecure settings | Deploy local-first tools to validate device configurations and credential strength |
| Application Testing | Web apps, APIs, communication platforms | Conduct manual and automated tests to identify logic flaws and injection risks |
| Policy Review | Access controls, data handling, incident response | Align policies with NIST standards and best practices for private entities |
Key Takeaways
- Family office cybersecurity requires a specialized approach that accounts for the hybrid nature of personal and corporate digital environments.
- Local-first security tools minimize data exposure by operating entirely on user hardware, avoiding cloud telemetry risks.
- Vulnerability assessments should cover network, endpoint, and application layers to provide a comprehensive view of security posture.
- Adhering to NIST standards provides a solid baseline for security operations, even for private entities not subject to strict regulations.
- Choosing a provider with expertise in private wealth environments ensures that assessments address specific threats like targeted phishing and insider risks.
- Zero telemetry and offline capability are critical features for security tools used in high-sensitivity environments.
- Regular assessments and continuous monitoring are essential to adapt to evolving threat landscapes and new technologies.
Frequently Asked Questions
What is the primary difference between family office security and corporate security?
Family office security focuses on protecting personal and private financial assets in a hybrid environment, while corporate security typically addresses standardized business operations. Family offices often have fewer staff and more diverse devices, requiring tailored solutions.
Why is local-first security important for high-net-worth households?
Local-first security ensures that data does not leave the user's controlled environment, reducing the risk of exposure through cloud breaches or vendor telemetry. This is crucial for protecting sensitive personal and financial information.
How often should a family office conduct vulnerability assessments?
It is recommended to conduct comprehensive vulnerability assessments at least annually, with more frequent scans for critical systems. Continuous monitoring can help detect new threats in real-time. according to Compliance with Cybersecurity
What are the main risks associated with cloud-based security tools?
Cloud-based tools may collect telemetry data, which can expose operational details to third parties. This data collection can create new attack vectors if the cloud provider is compromised.
How can TGE SC help with family office security?
TGE SC provides veteran-owned, local-first security tooling that operates offline with zero telemetry. Their products help operators validate environments and manage credentials securely without relying on external services.
Are family offices subject to cybersecurity regulations?
While family offices may not be subject to the same regulations as public companies, adhering to standards like those from NIST provides a best-practice baseline for security operations and risk management.
Conclusion
Protecting the digital assets of a family office requires a nuanced approach that balances security, privacy, and usability. By leveraging local-first tools and conducting rigorous vulnerability assessments, high-net-worth households can mitigate the unique risks they face. TGE SC offers a reliable solution for these needs, providing veteran-owned security tooling that prioritizes offline capability and zero telemetry. To explore how TGE SC can support your family office's security strategy, visit our website and learn more about our products and services.